Scope and coverage record
Records what each scan had in scope and what it scanned, failed or excluded. Files and tables IRIS couldn’t read carry a reason, and a missing figure reads as unknown.
Audit evidence. Evidence register. Framework reports.
IRIS records the scope of each dated scan, links each finding to its source and keeps an evidence register your auditor can test, with the gaps listed.
Seven fields from the sample report, a real IRIS scan of a database, with what your auditor can test in each.
| Field | In the sample report | What your auditor can test |
|---|---|---|
| Source scanned | enterprise_data · database · 2 schemas (iris_dataset, public) | The population: the findings cover these two schemas and nothing else |
| Objects in scope | 16 tables · 190 columns | Completeness: reconcile the tables in scope with the database’s own catalog |
| Scan | October 26, 2026, 15:05 to 15:09 · status completed | The run behind every finding; had a table been unreadable, the status would read partial |
| Scan history | 22 completed scans of this source, September 18 to October 26, 2026 | A period: each scan shows the condition on its own date, and the days between stay unobserved |
| Coverage and gaps | marketing_contacts returned 0 rows; its columns were classified from names and types only | Which results rest on column names alone, so you sample those differently |
| Key finding | user_credentials.api_key · Credential · protection: none detected · 15 rows | The exact column to inspect, and the protection state found in the samples |
| Evidence register | Classification report · IRIS-generated · under review | That no person has approved the item yet |
Evidence from the sources you connect. Mapping shows where a finding is relevant; your auditor decides what it proves.
Records what each scan had in scope and what it scanned, failed or excluded. Files and tables IRIS couldn’t read carry a reason, and a missing figure reads as unknown.
Generates evidence items from scan data into a register your team reviews and exports as CSV or XLSX, each with its generated date, scope and reviewer decision.
One unified control framework maps six frameworks: GDPR, HIPAA, CCPA/CPRA, India’s DPDP Act, the RBI Cybersecurity, Technology Risk, Resilience and Assurance Framework Directions and SEBI CSCRF.
Runs scans on a schedule or on demand before an audit. Each scan is dated, so a series of scans shows the condition across a period.
Builds reports that show findings and evidence by framework, for an auditor, a regulator or a customer’s security review.
Shows for each control whether evidence is present, missing or deferred. Your team marks each control, and your auditor decides whether it is met.
Capabilities vary by edition.
Choose the sources and frameworks for this audit. Anything left out is recorded as a gap.
IRIS scans the connected sources and records the coverage of each one.
Findings and evidence are mapped to controls in the frameworks you enable.
Your team marks each control and exports the evidence register and reports.
After a fix, a re-scan records the new condition with its own date.
Findings listed by database, schema, table and column, each linked to the scan that produced it and that scan’s coverage record.

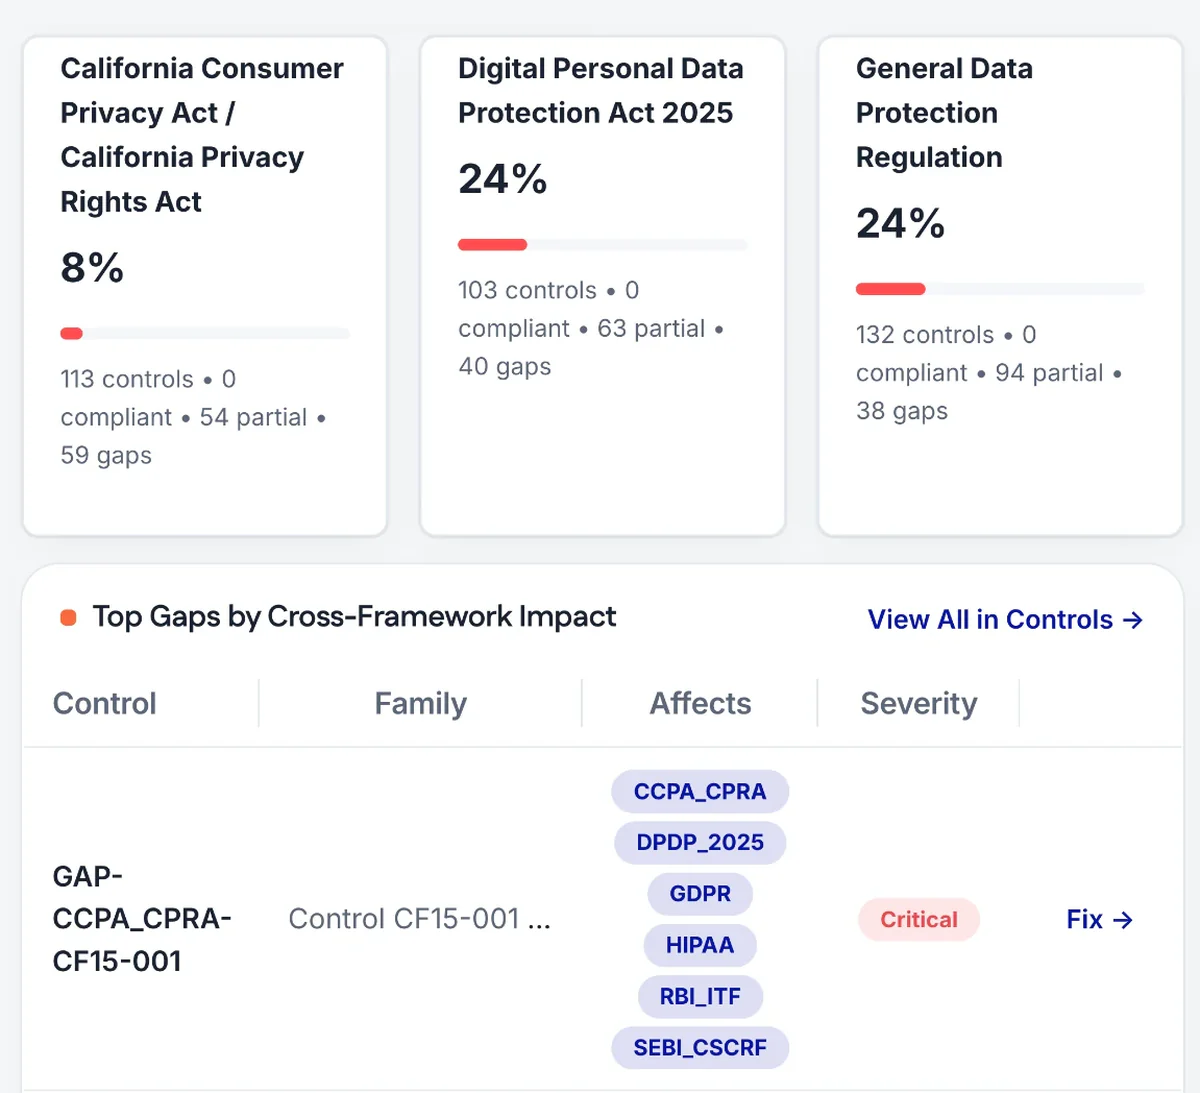
A score for each framework, and the control gaps that affect several frameworks at once. Each control shows whether evidence is present, missing or deferred.
Mapping shows relevance; your auditors judge whether a control is met.
373
controls in one unified framework
756
mappings between controls and frameworks
176
controls serving two or more frameworks
So one piece of evidence can serve several
The scope record lists each source and what was scanned, failed or excluded, with reasons. Sources nobody connected sit outside it, so list them beside it.
The reviewer’s decision and its date. A machine finding stays pending until a person decides it, and a decline needs a reason.
One scan covers one date. For a period, show the series of scans across it, and treat the days between them as unobserved.
A closed ticket isn’t proof that the risk changed. A successful re-scan is.
Auditors test information an organization produces before they rely on it. ISA 500, paragraph 9, asks for evidence that it is complete and correct, and PCAOB AS 1105.10 asks the same of US public-company auditors.
For completeness, give your auditor the scope record and the list of unread tables to reconcile with the source’s own catalog. To check it’s correct, let them agree a sample of findings to the tables and columns named.
In the audits Dipal Panchal describes, the answers still arrive by email and the auditor files them by hand. To see where each field above is written, follow one scan on the how-it-works page.
The laws and frameworks IRIS scores, and those where it maps evidence without a scored view.
How internal audit teams use IRIS evidence for the data part of an audit.
Data subject requests searched across connected databases, with changes made in the source system.
Your auditor decides what is sufficient. In Dipal Panchal’s words: “Can we certify whether that evidence is correct? That’s the auditor’s job.”
The evidence register as CSV or XLSX, the framework reports, and the scope and coverage record for each scan. The sample report shows the layout.
The date and time of the scan that produced it. Each scan’s findings are kept, so a re-scan adds new dated findings beside the earlier ones.
The six in the control set above. For other laws and standards, IRIS maps its evidence to their controls through its unified compliance framework. A scored readiness view for those isn’t in v1; ask us if you need one. Explore compliance
Yes. The coverage record lists what was scanned, what failed and what was excluded, with the reason for each.
Bring the question your last auditor asked. We’ll show you the evidence IRIS produces for it.